
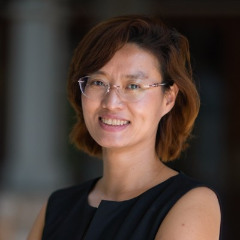
This inventor holds 3 USPTO granted patents and 1 published patent application. Top assignees: Virginia Tech Intellectual Properties Inc., Rutgers, The State University of New Jersey. Active years: 2014-2026.
Data source: USPTO (United States Patent and Trademark Office) public patent records. Weekly synchronization. How IDiyas builds this profile
Company Filing History:
 2 out of 824
 1 out of 1,496
Years Active: 2014-2026
Title: Danfeng Yao: Innovator in Insider Threat Detection and Malware Analysis
Introduction
Danfeng Yao is a prominent inventor based in Blacksburg, VA (US), known for his significant contributions to the fields of cybersecurity and threat detection. With a total of 3 patents, Yao has developed innovative technologies that address critical challenges in identifying insider threats and distinguishing between legitimate and malicious network traffic.
Latest Patents
One of Yao's latest patents is focused on "Probabilistic evidence based insider threat detection and reasoning." This technology utilizes probabilistic programming-based computation strategies, which excel in managing uncertainties when identifying anomalous patterns. The ability to handle uncertainties is particularly crucial for detecting insider threats, as these situations often lack clearly defined rules and policies. The probabilistic model identifies deviations from normal behavior and elucidates the computational path of these deviations. The result interpretation unit allows organizations to investigate the causes with high accuracy, thereby minimizing costly and embarrassing false alarms. Additionally, this technology ranks abnormal events, which aids in prioritizing follow-up manual investigations.
Another notable patent is for the "Detection of stealthy malware activities with traffic causality and scalable triggering relation discovery." This invention involves a computer system designed to differentiate between user-initiated network traffic and malware-initiated traffic. The system comprises at least one central processing unit (CPU) and a memory that is communicatively linked to the CPU. The memory contains program code that monitors individual network events to ascertain whether each event has a legitimate root-trigger. Malware-initiated traffic is identified as an event lacking a legitimate root-trigger, enhancing the ability to detect malicious activities.
Career Highlights
Danfeng Yao has worked with notable institutions such as Virginia Tech Intellectual Properties Inc. and Rutgers, The State University of New Jersey. His work at these organizations has significantly contributed to advancements in cybersecurity technologies.
Collaborations
Yao has collaborated with esteemed colleagues, including Chehai Wu and Deian Stefan, further enriching his research and development efforts in the field.
Conclusion
Danfeng Yao's innovative work in insider threat detection and malware analysis showcases his expertise and commitment to enhancing cybersecurity measures. His patents reflect a deep understanding of the complexities involved in identifying and mitigating threats in digital environments.
Data source: USPTO (United States Patent and Trademark Office) public patent records. Weekly synchronization. How IDiyas builds this profile